Sheila Gulati Warns AI Security Investment Is Lagging Behind Rapid Enterprise Adoption
Image: Bankinfosecurity
Main Takeaway
Sheila Gulati says AI security remains woefully underfunded as enterprises accelerate adoption, while investors confront weak exits and unreliable deployment foundations.
Jump to Key PointsSummary
Gulati’s central warning
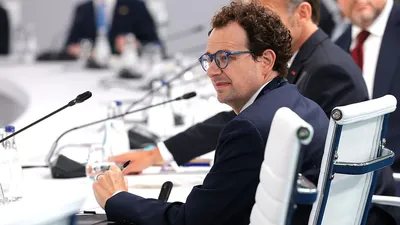
AI security investment is falling far behind the speed of AI adoption, Sheila Gulati said in a Bloomberg interview. Gulati, founder and managing director of Tola Capital and a former Microsoft Azure leader, framed the gap as a strategic weakness for companies building and deploying increasingly capable systems.
Her warning lands as investors remain bullish on enterprise AI but face a market where security products, governance tools, and infrastructure are still being tested. Gulati’s background spans cloud computing and enterprise software, giving her view a platform-investor perspective rather than a narrow product pitch. GeekWire’s profile described her as an investor assessing startups during another major technology transition, while an AI biography traces her work from Microsoft’s cloud strategy to enterprise applications.
Why the funding gap matters
The underinvestment affects more than model protection. AI security includes access controls, data handling, model monitoring, software supply chains, prompt and agent defenses, and the governance needed to assign responsibility when systems act unpredictably.
Financial executives face a related problem: spending on security products does not produce reliable protection when data quality, internal controls, and organizational ownership are weak. The Financial Executives Journal argues that AI initiatives fail at high rates when foundational governance is missing. That concern aligns with Gulati’s broader warning, while Bankinfosecurity shows the commercial tension on the other side: AI security funding has expanded sharply, but profitable exits remain uncommon.
Investors face a difficult market
AI security has attracted capital, yet investment volume alone has not created a mature category. Bankinfosecurity describes a pattern of early funding followed by rapid exits and limited evidence of durable returns, placing pressure on founders to prove that products solve urgent operational problems rather than simply attach security language to an AI platform.
Gulati’s investment lens connects that market test to enterprise demand. Security startups need buyers with budgets, clear risk owners, usable deployment paths, and measurable outcomes. The broader AI investment case remains strong, according to GeekWire’s account of Gulati’s approach, but enthusiasm for AI does not remove the need to distinguish durable infrastructure from crowded experimentation.
Governance must keep pace
Governance is becoming a technical requirement for AI security, not a separate compliance exercise. Companies need policies for model access, training data, vendor risk, human review, incident response, and the authority granted to autonomous or semi-autonomous agents.
The Financial Executives Journal places governance, data, and organizational readiness at the center of successful AI security deployments. That emphasis gives practical shape to Gulati’s funding warning: more money helps only when companies know which systems require protection and how to measure whether controls work. The Turing Centre page, although largely inaccessible in the supplied capture, points to a parallel resilience discussion around frontier AI under pressure.
What enterprise buyers should demand
Enterprise buyers should treat AI security as an operating layer that follows models into applications, workflows, and third-party services. Procurement teams need evidence of data isolation, audit trails, identity controls, testing against adversarial behavior, and clear procedures for disabling or correcting an AI system.
They also need to examine whether a vendor can support deployment beyond a pilot. Bankinfosecurity’s account of weak exits highlights the commercial risk of selecting products that lack staying power, while the financial governance analysis warns that poorly prepared organizations can turn security spending into another failed AI initiative. Gulati’s message therefore reaches both sides of the transaction: investors need disciplined diligence, and customers need measurable controls.
The next phase of AI security
AI security will become more consequential as enterprises connect models to sensitive data, business systems, and automated decision processes. That expansion raises the cost of weak identity management, poor monitoring, and unclear accountability, even when a model itself performs as advertised.
The immediate test is whether capital shifts toward products that reduce concrete operational risk rather than toward generic AI branding. Gulati’s warning, the uneven startup outcomes described by Bankinfosecurity, and the governance failures outlined for financial leaders all point to the same requirement: security must be funded, embedded, and measured alongside AI deployment.
Key Points
Sheila Gulati warns AI security funding is lagging behind rapid enterprise adoption and expanding system risks.
Enterprise AI security fails when governance, data quality, and organizational ownership remain weak.
AI security funding is rising, but startups still struggle to produce profitable exits and durable products.
Investors are separating essential security infrastructure from crowded AI applications with limited operational value.
Enterprise buyers need measurable controls for identity, data isolation, monitoring, testing, and incident response.
Questions Answered
Sheila Gulati is the founder and managing director of Tola Capital and a former Microsoft Azure leader. She said the AI industry is woefully under-invested in security as enterprise adoption accelerates.
Sheila Gulati says security investment is lagging behind the speed and scale of AI deployment. Companies are connecting models to sensitive data and business systems before governance, monitoring, and accountability are mature.
AI security startups are attracting significant funding, but profitable exits remain uncommon. Bankinfosecurity reports that the market has seen strong deal activity alongside rapid failures and uncertain commercial durability.
Companies should evaluate data isolation, identity controls, audit trails, model monitoring, adversarial testing, vendor resilience, and incident response. They should also confirm that the product works beyond a limited pilot.
Governance determines who controls AI systems, how data is handled, and what happens when a system fails. Weak governance can turn a security purchase into another unsuccessful AI initiative.
Source Reliability
25% of sources are highly trusted · Avg reliability: 65
Go deeper with Organic Intel
Simple AI systems for your life, work, and business. Each one includes copyable prompts, guides, and downloadable resources.
Explore Systems